Compliance you can prove
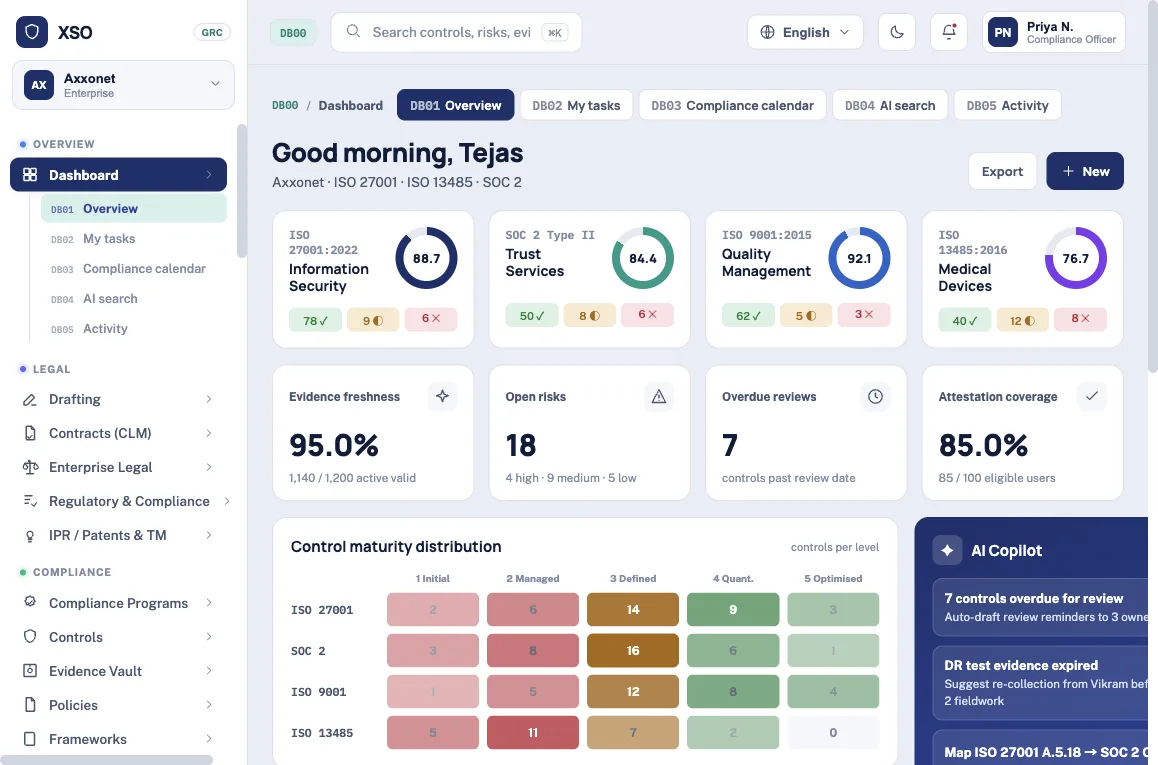
XSO replaces spreadsheet compliance with a live operating system: map controls once, reuse them across standards, keep evidence fresh, and give auditors secure self-service access to the current state of your program, across ISO 27001, ISO 9001, ISO 13485, SOC 2 Type II, 21 CFR Part 11 and ALCOA+.
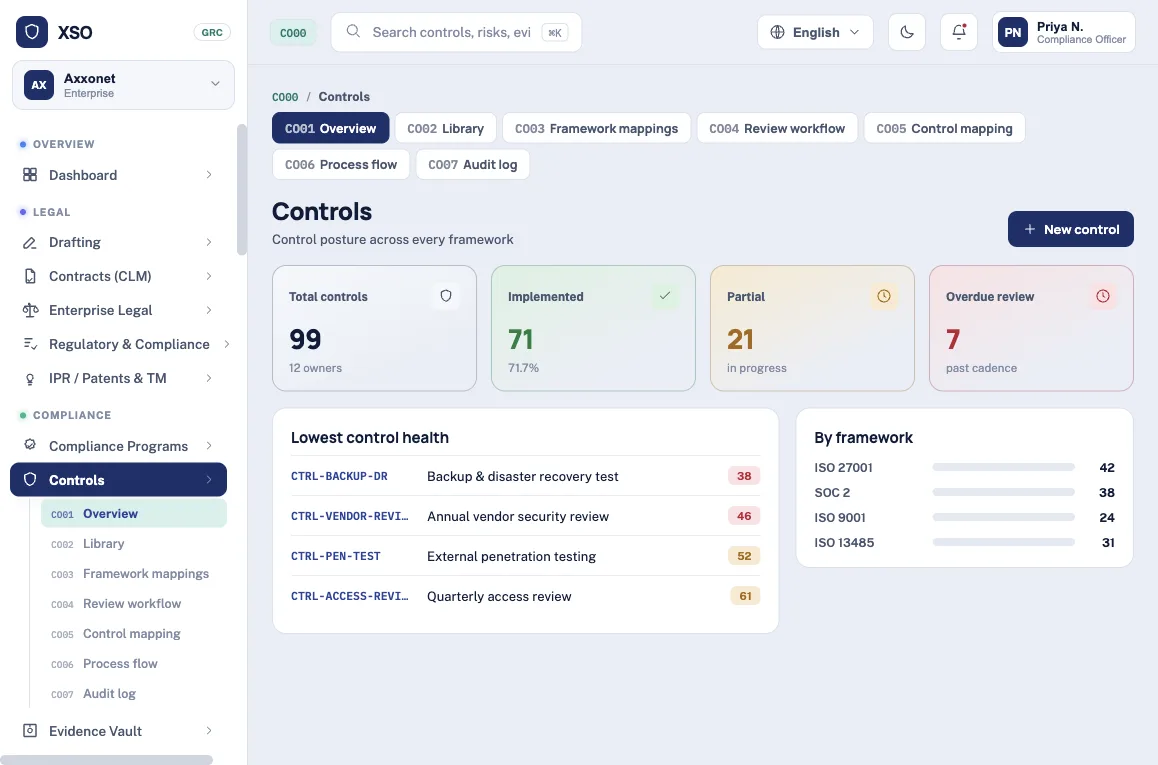
Multi-framework control library
Link ISO, SOC 2, QMS and medical-device obligations to a shared control set so teams stop duplicating work, with ownership, review cadence, maturity and reusable cross-standard mappings.
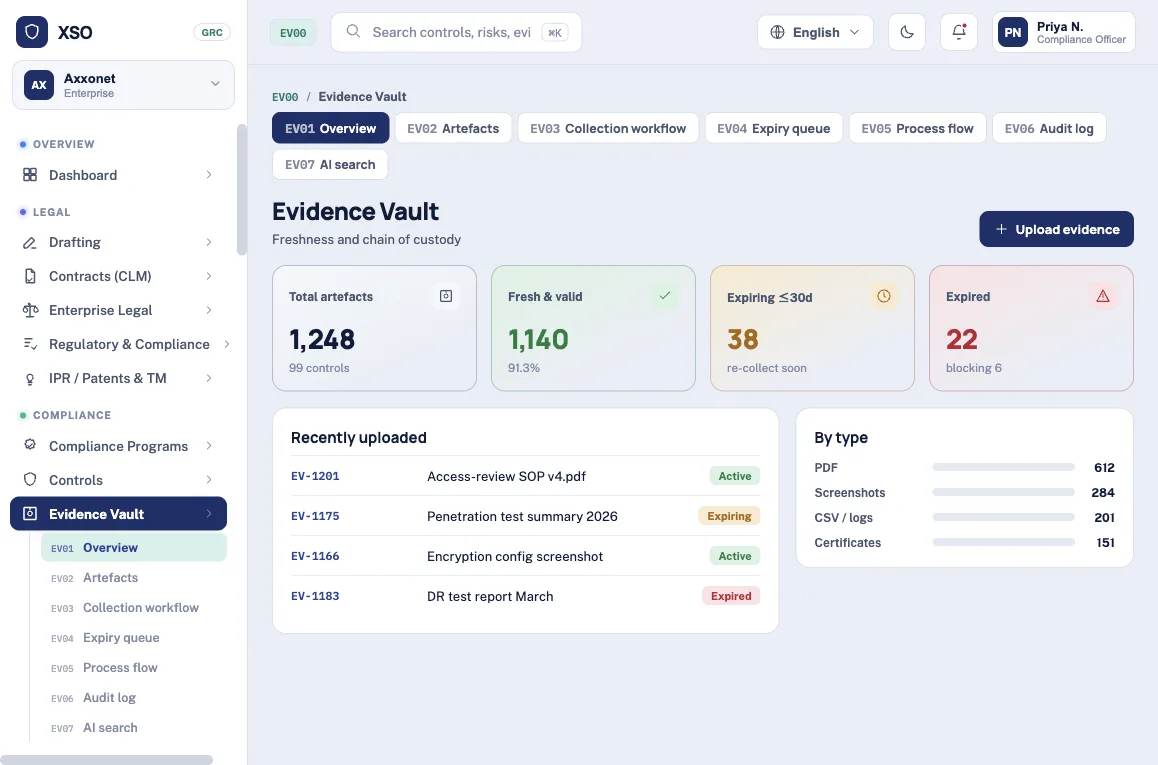
Evidence vault with expiry tracking
Hash, classify, bind and review evidence while the vault automatically surfaces stale or missing artefacts, tracks freshness and validity, and drives an expiry queue and collection workflow toward audit-ready coverage.
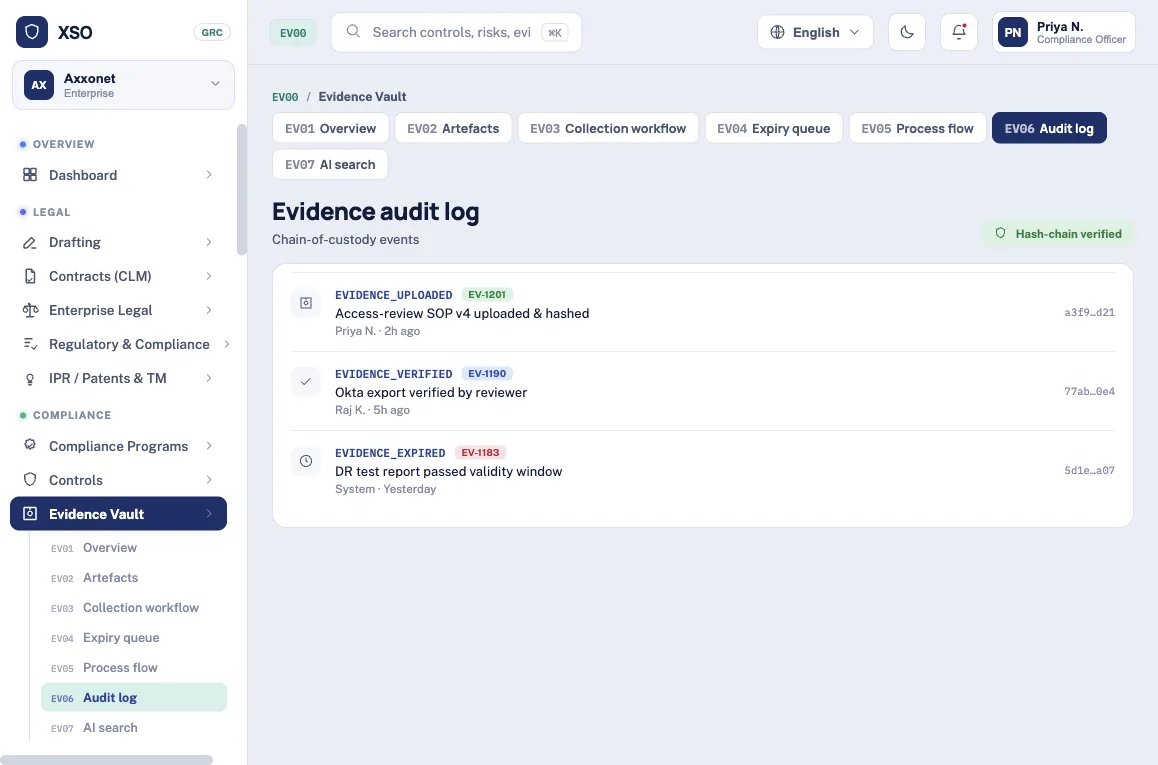
Immutable, hash-chained audit trail
Every mutation is captured in a tamper-evident audit log. Each event records a SHA-256 previous-hash chain with verification endpoints, making policy, control, evidence and risk changes defensible under tenant isolation and traceable ownership.
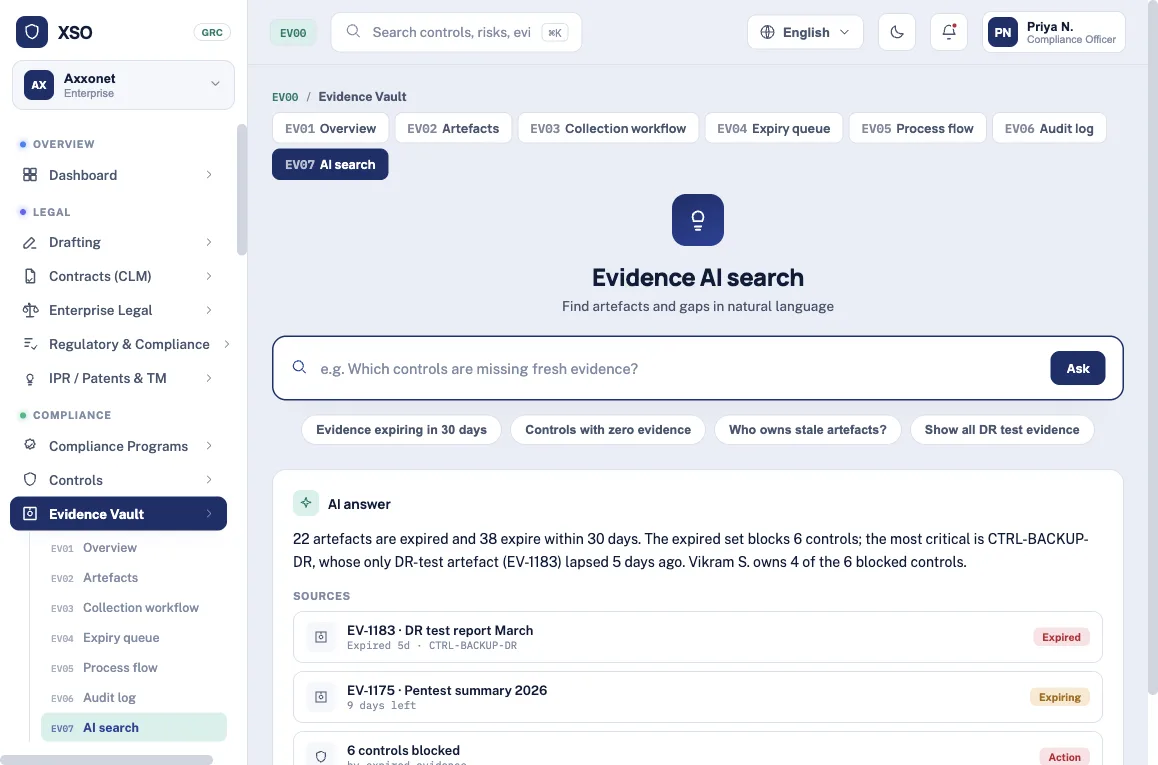
AI-assisted search
Ask questions in natural language and get answers with linked controls, risks, evidence, owners and audit context, surfacing expiring evidence, controls with zero evidence, and blocked controls at a glance.
Built for regulated teams
Strict tenant isolation (PostgreSQL row-level security), OIDC/Keycloak role-based access, immutable audit logging, and an automation-ready integration layer (a Microservices Engine, FastAPI services, MinIO evidence storage, Redis queues and metrics endpoints).